Your people data, properly protected
HR holds the most sensitive records a company keeps: salaries, identity documents, grievances, medical absences. Savanna360 is built so that access is proven rather than assumed, and every consequential action leaves a record nobody can quietly edit.
What is in place
Isolated workspaces
Every customer gets their own database and their own subdomain. There is no shared table and no cross-tenant query path.
Encryption everywhere
TLS in transit with certificates renewed automatically, and encryption at rest on the underlying storage.
Multi-factor authentication
One-time codes on login, on password reset, and before sensitive actions such as a wage draw.
Append-only audit log
Approvals, payroll submission, access and password changes, loan decisions and grievance reviews, each with actor, time and source.
Role-based access
Enforced on the server, not hidden in the interface. A manager cannot query outside their reporting line.
In-region hosting
Data stays on infrastructure Techsavanna operates in your region, rather than being shipped to another continent.
Proven, not assumed
Authorisation is checked on the server for every request. Hiding a button is not security, so the same rule that greys out a screen also refuses the API call behind it.
- Role and reporting-line scope enforced server-side
- Salary and document access restricted independently of general HR access
- Sensitive mobile screens can require a fingerprint or face unlock
- Session tokens rotate, and a lost device can be revoked from the account
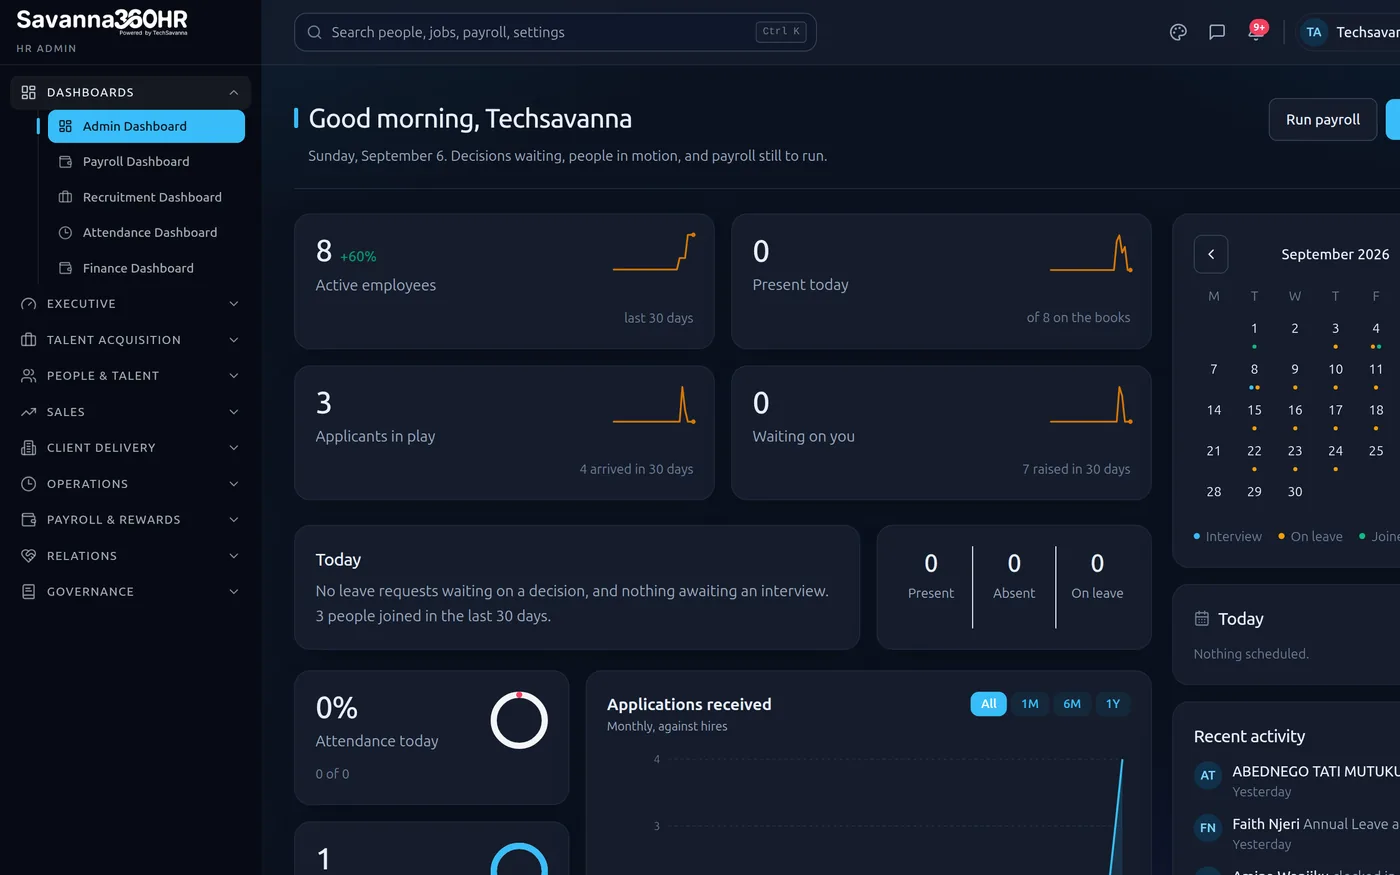
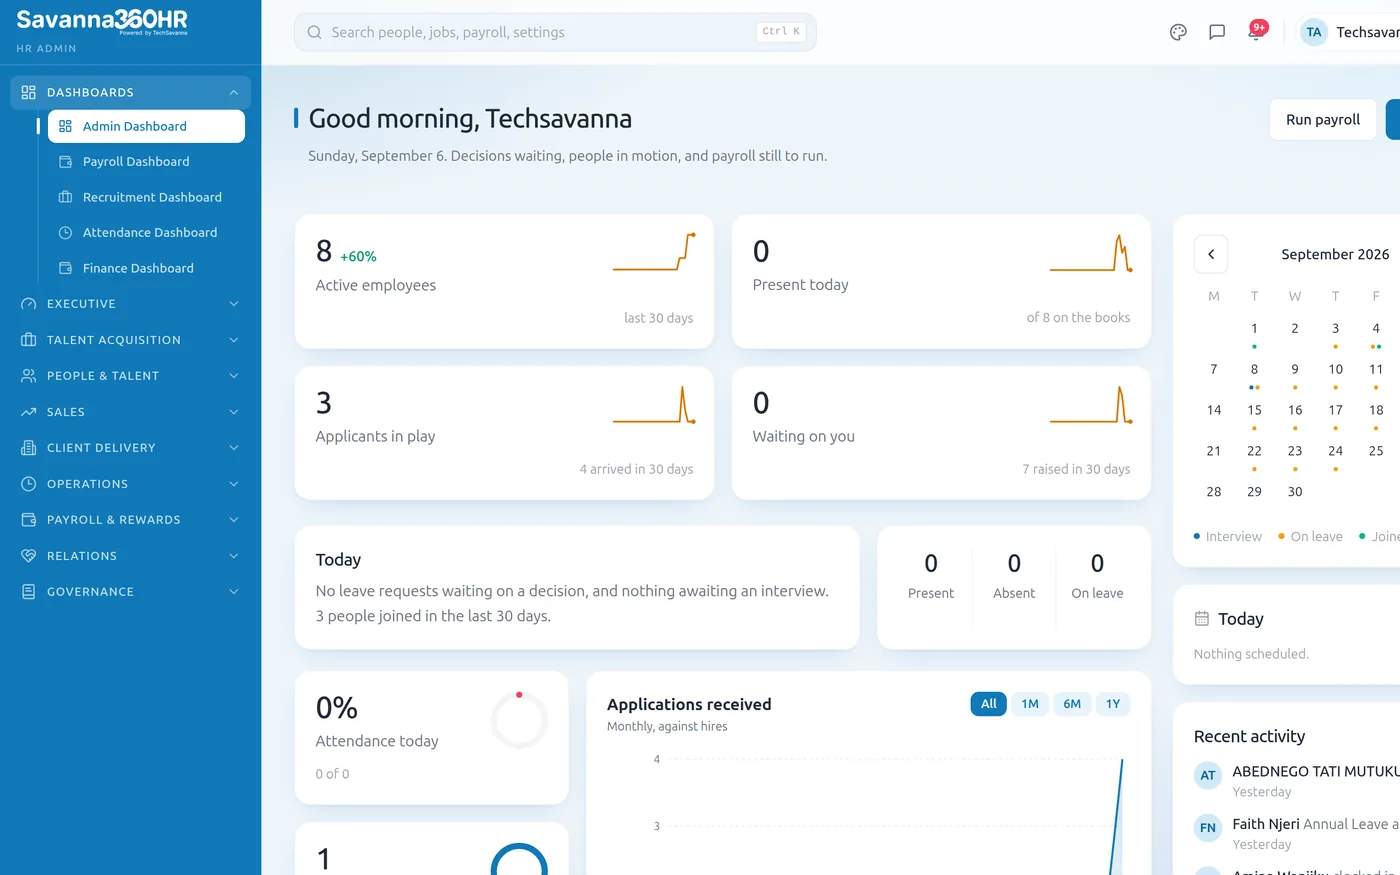
Access is enforced in the live workspace
A record nobody can edit
The audit log is append-only. Entries cannot be amended or deleted, including by an administrator, so an investigation months later has something dependable to read.
- Every approval, payroll submission and access change recorded
- Actor, timestamp, source address and what changed
- Exportable as an evidence pack for auditors
- Retained for the statutory period even after an employee exits
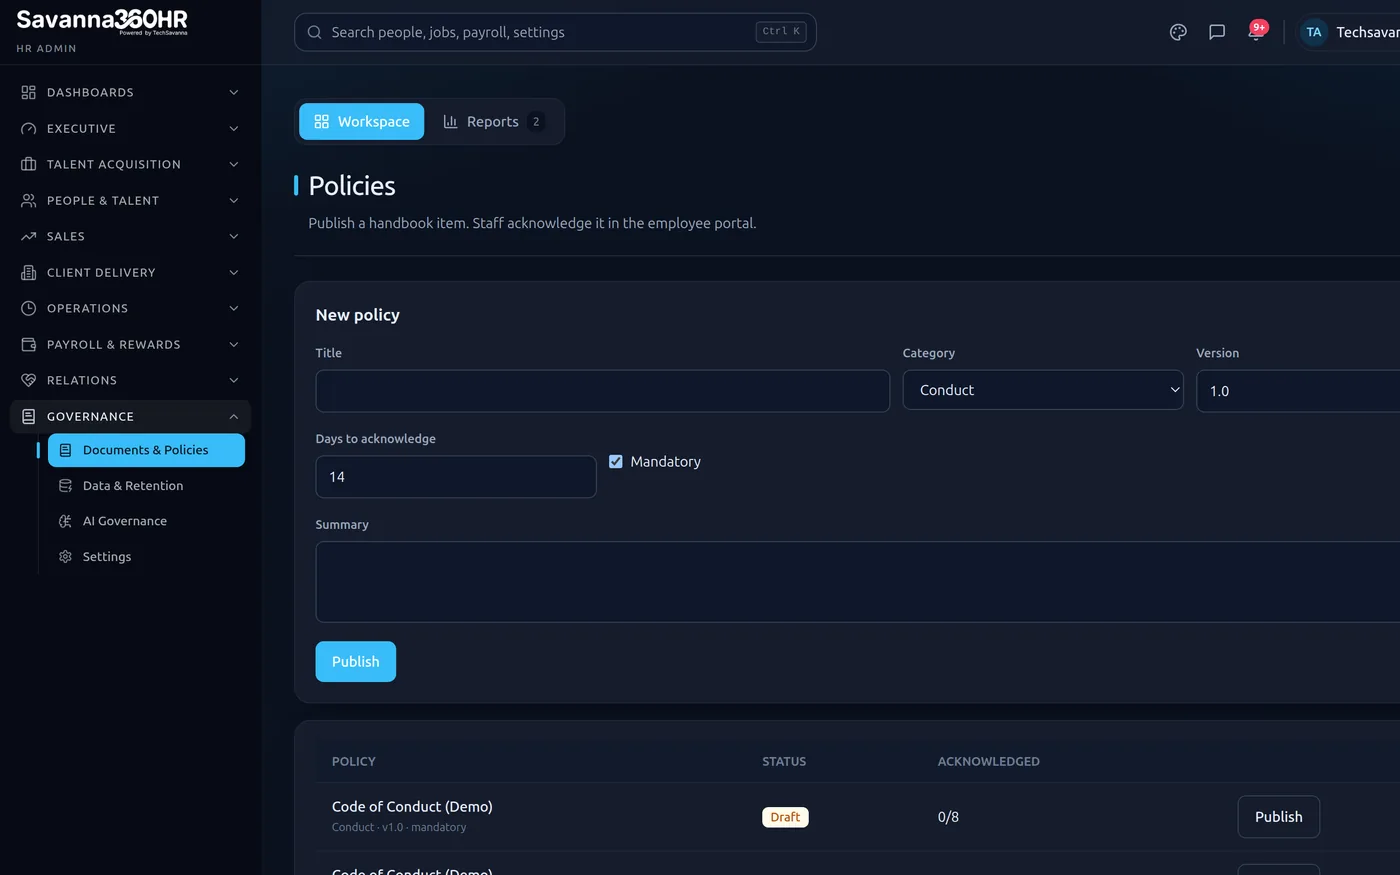
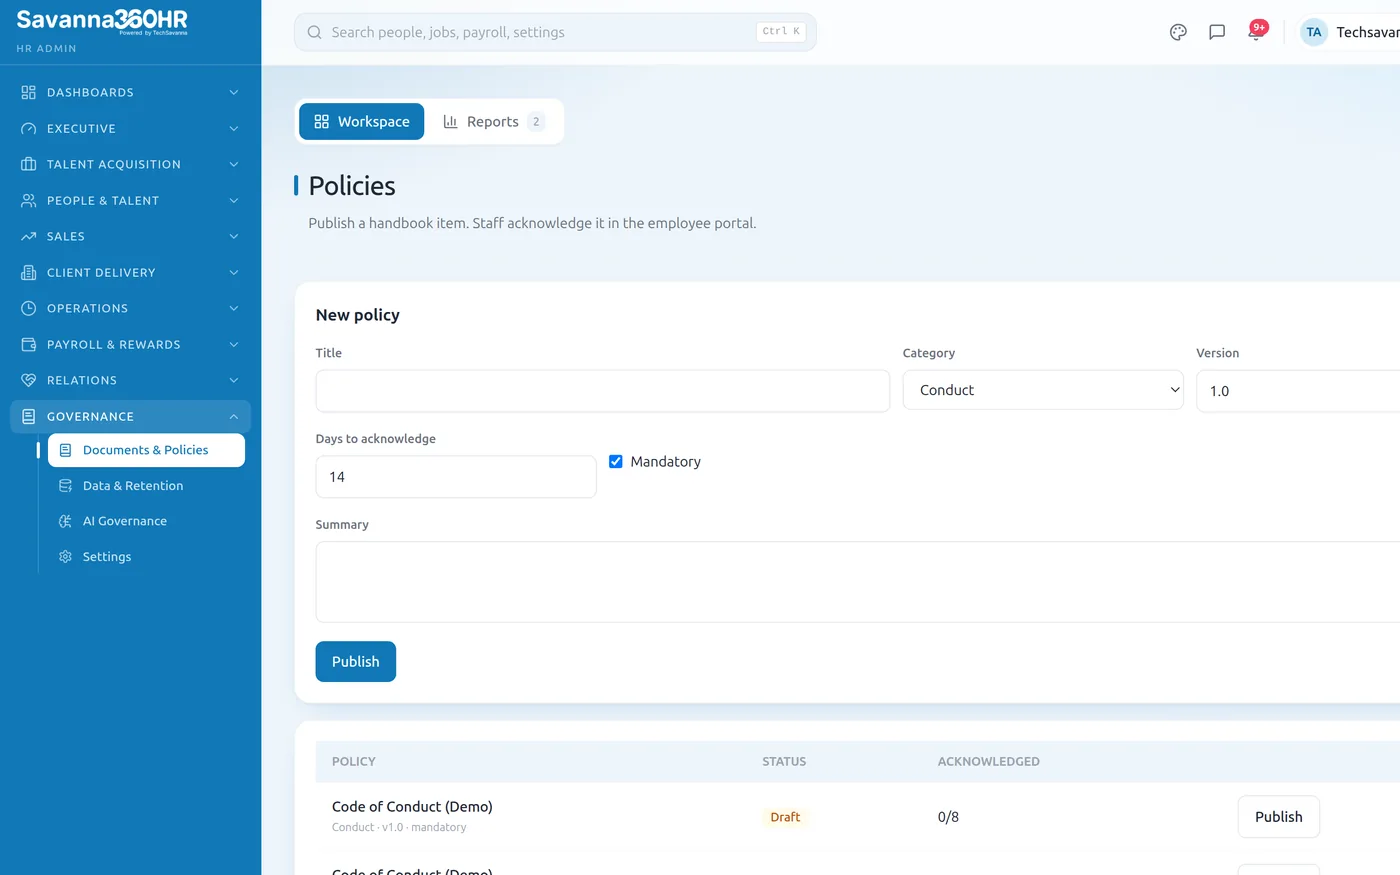
Documents and changes stay on the record
Sensitive channels stay sensitive
A grievance is not an ordinary support ticket. Anonymous submissions stay anonymous, attachments move through a permissioned channel rather than a public link, and only assigned reviewers can open a case.
- Anonymous submission that HR cannot de-anonymise
- Attachments served through an authenticated channel, never a public URL
- Case access limited to assigned reviewers
- Employee consent required before colleague messaging
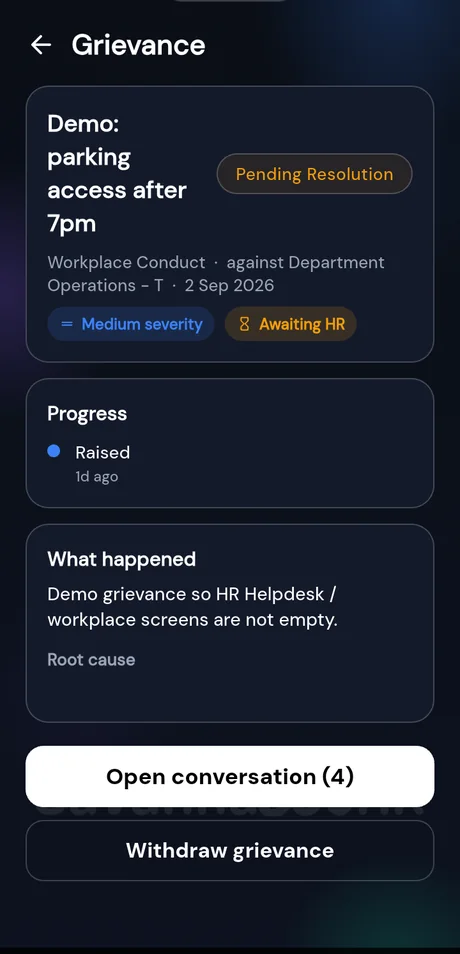
What Techsavanna holds, and what we design to
We separate the two deliberately. The first group are credentials Techsavanna actually holds; the second are the regimes the platform is built to let you satisfy as the data controller.
Certifications held by Techsavanna
Data protection, registered
Registered with Kenya’s Office of the Data Protection Commissioner as a Data Processor, and built to the Kenya Data Protection Act, 2019.
ISO 9001:2015 certified
Quality management certified by Gabriel Registrar, certificate GR25-301707 — the process behind how the platform is built, delivered and supported.
UAF / IAF accredited
That ISO certificate is issued under the United Accreditation Foundation and carries the IAF Multilateral Recognition mark, recognised internationally.
Oracle partner
A registered Oracle partner (Member, Level 1); the Techsavanna team also holds Oracle Cloud Infrastructure certifications.
Regimes the platform is designed for
Savanna360 HR gives you the controls and the evidence these require. Compliance itself rests with you as the data controller; we are your processor.
How the platform is run
Automatic certificate renewal
TLS certificates renew automatically well before expiry, with an independent daily check and an alert if anything is ever at risk.
Self-healing provisioning
A workspace build that hits a transient fault retries on its own, and a stalled build is detected and recovered by a watchdog.
Continuous monitoring
Platform health, job queues and disk are monitored continuously, with alerting to the operations team.
Backups and export
Regular backups of every workspace, plus on-demand export of your own data at any time.
Frequently asked questions
No. Each customer workspace has its own database and its own subdomain. There is no shared application table holding several customers' employees, and no query path from one workspace to another.
On infrastructure operated by Techsavanna in your region. Data is not replicated to another continent for processing, which is what keeps the Kenya Data Protection Act and POPIA residency expectations satisfiable.
Access to production is limited to named operations staff, requires multi-factor authentication, and is logged. Support staff do not have standing access to customer records; access for a specific support case is time-bound and recorded.
Yes. MFA can be required for all users, or for specific roles such as HR and payroll administrators. It is enforced at login and again before sensitive actions.
Approvals and rejections, payroll submission, password and access changes, loan and advance decisions, grievance reviews, and administrative configuration changes. Each entry records the actor, the time, the source address and what changed. Entries cannot be edited or deleted.
You export it first, in full, at any point before or after cancellation. After the retention window your workspace and its database are removed. We do not retain a copy for our own purposes and we never sell or repurpose customer data.
Yes. Sign-in can be delegated to your identity provider over OAuth or LDAP, so access follows your existing directory and de-provisioning is immediate when someone leaves. Configuration is done with you as part of Enterprise onboarding.
Email support@techsavanna.technology with the details. We acknowledge, investigate, and keep the reporter informed through to resolution.
See the controls on your own workspace
Provision a trial workspace and inspect the audit log, the roles and the access rules yourself.